

One architecture that adapts to many scenarios
For decades, Multi-Protocol Label Switching (MPLS) was the backbone of enterprise networking — dedicated, predictable, and secure by design. But the way organizations operate has changed faster than that model can keep up with. Cloud adoption, the explosion of SaaS platforms, and a workforce that’s no longer tied to a desk have all but rewritten the rules of network architecture.
We sat down with Laura Askew, co-founder of Criticalis, to talk through what’s driving the shift to SD-WAN (Software Defined Wide Area Networks) and SASE (Secure Access Service Edge), what “secure business anywhere” really means, and what organizations need to know before making the leap.
Why This Shift Is Happening Now
Enterprise infrastructure has changed significantly over the past several years. Historically, organizations hosted applications on-premises or in data centers, and MPLS provided dedicated, secure point-to-point links between locations. That model made sense when everything connected back to a central location.
Three major shifts have disrupted it. First, the migration to cloud services. Second, the widespread adoption of SaaS platforms like Office 365 and Salesforce, hosted by third-party vendors rather than internally. And third, the dramatic rise in remote work, accelerated by COVID-19. Together, these changes eliminated the need for users to connect through a central point at all.
“The shift toward SASE is driven by three major trends: cloud migration, growth of SaaS services, and the rise of remote working.” – Laura Askew, co-founder, Criticalis.
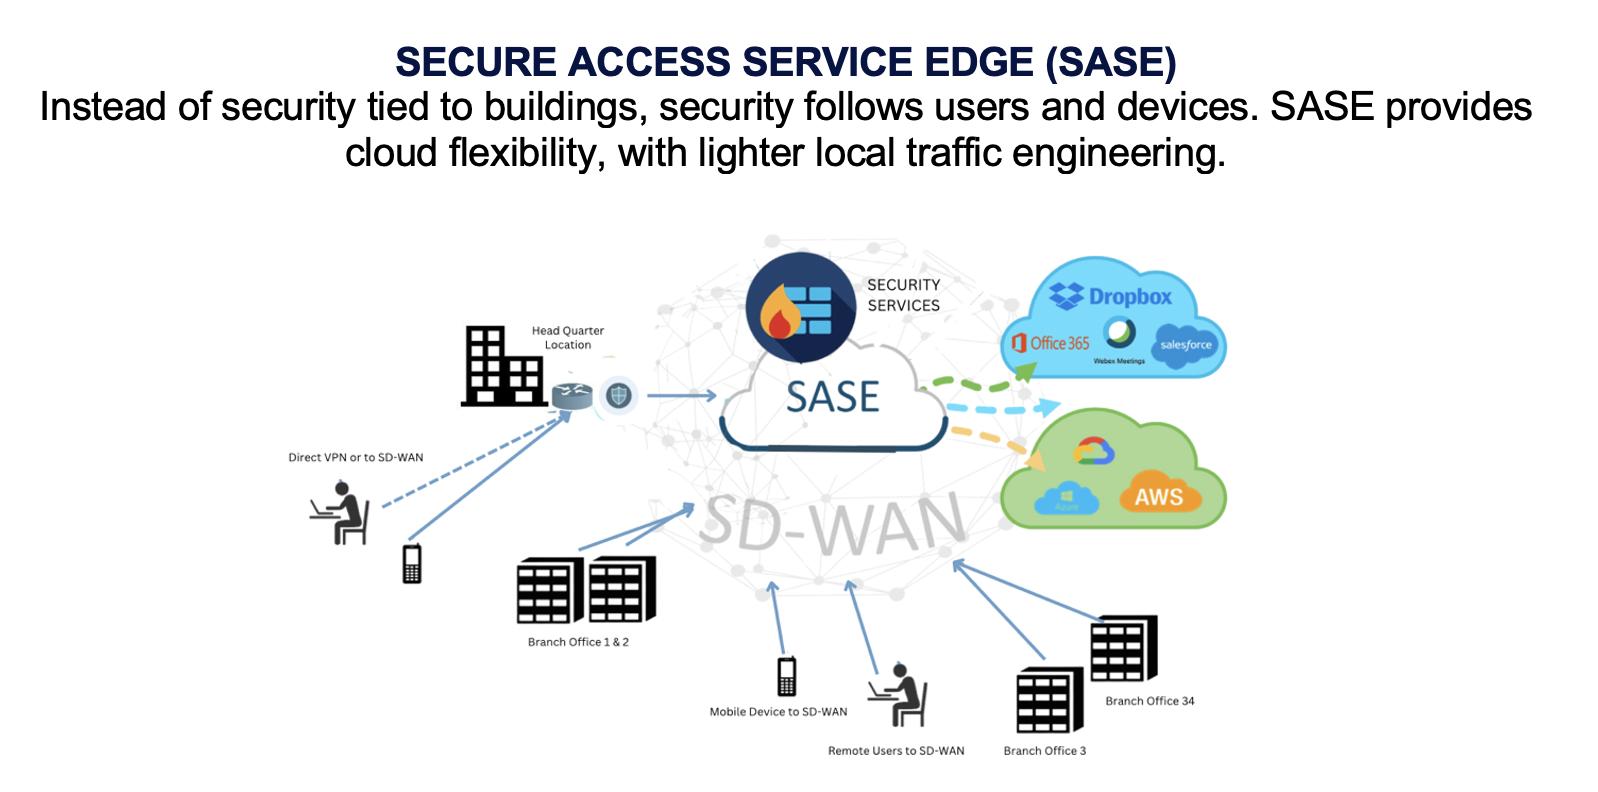
SASE actually emerged as an enhancement to SD-WAN, adding security functions delivered as a cloud service. The ideal use case was to position SASE as a replacement for remote access VPNs. It’s since evolved into something much broader — a framework that consolidates multiple point products and a full security stack (including ZTNA) into a single, unified platform. As a result, on-premises firewalls at branch locations can often be scaled back, with SASE handling connectivity and security across distributed environments instead.
Defining SASE: Secure Access Service Edge
- SASE is a cloud-native architecture that unifies SD-WAN with security functions like SWG, CASB, FWaaS, and ZTNA into one service.
- By consolidating networking and security functions into a single, cloud-delivered service, SASE simplifies network management and enhances security.
- The architecture supports the dynamic needs of modern organizations by providing scalable, unified access and protection for distributed environments.
SASE providers also offer globally distributed points of presence, allowing organizations to tunnel traffic over a shared backbone and emerge at local endpoints, wherever those happen to be. That eliminates the need to procure and manage dedicated lines, which offers a lot more flexibility. Something that would have seemed impractical five or ten years ago — like a fully mobile remote worker with no fixed connection point — is now not just architecturally feasible, but often the more logical approach given how infrastructure has evolved.
The MPLS-to-SD-WAN Transition
Think of this transition as a change in the nature and location of risk. For example, when you route traffic over a provider’s backbone, you’re introducing a dependency on that provider’s infrastructure. It’s similar to how a cloud outage at a major provider like AWS can cause downstream disruptions.
Organizations need to conduct thorough risk assessments to understand how risk is shifting, not simply whether risk exists. Modern SASE tools have matured a great deal and provide genuinely robust security functionality. The critical step is understanding what the new architecture actually looks like, and designing it deliberately, with a clear-eyed view of the risks that come with it.
“Organizations considering SASE transitions should begin with a thorough assessment of their architecture, requirements, and risk profile — before selecting technology.” – Laura Askew, co-founder, Criticalis
Organizations operating in environments where data confidentiality and integrity are absolutely paramount may need to exercise more caution. That said, those industries are typically already conducting rigorous risk assessments and have in-house security teams actively weighing these decisions.
For most industries, the transition can be made safely, provided the risk evaluation is thorough. In high-sensitivity environments, the primary concern really comes down to confidentiality risk.
Zero Trust + SASE
For decades, network security worked like a castle with a moat. Once you were inside the corporate network, plugged into the office, connected via VPN…you were trusted. That model doesn’t hold up anymore, and it’s exactly the gap Zero Trust and SASE were built to close.
Zero Trust originated as a network architecture concept built on a simple principle: grant the least privilege necessary, and never trust by default. It started out fairly coarse — implemented through network segmentation, controlling which systems could talk to which. Over time, it’s become far more granular, enabling user-level and application-level policy enforcement. A specific employee — let’s call him Bob — can be granted access only to the resources required for his role, with read-only rather than read-write permissions where appropriate. That limits the “blast radius”: the potential damage if Bob’s account is ever compromised.
SASE is the architecture that makes that principle workable at scale. Instead of depending on which network the user happens to be accessing, the same security rules and policies follow the user wherever they are working, creating one consistent, unified framework for all users.
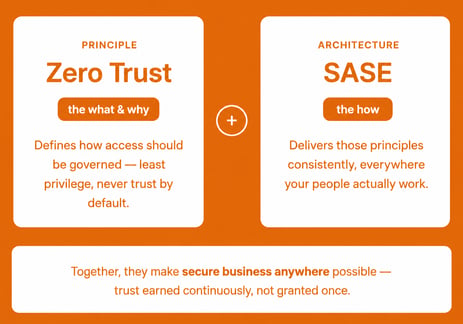
“Zero Trust and SASE are complementary. Zero Trust isn’t a product you buy; it’s a set of principles about how access should be governed. SASE is the delivery mechanism — the framework that actually enforces those principles consistently, across a distributed environment. You need both: a sound architecture to operate within, and clear policies governing what happens inside it.” – Laura Askew, co-founder, Criticalis
Neither fully replaces the other — together, they’re what makes “secure business anywhere” actually possible.
Practical Guidance for IT and Security Leaders – the first 90 days
Where do organizations begin to evaluate a transition? Start by clearly defining what you’re actually trying to achieve. That means a thorough assessment of your current infrastructure — how many sites you have and what each one looks like, what applications and connectivity are genuinely needed at each location, and how users actually traverse the network day to day.
Under a SASE model, smaller remote sites may only need a stripped-down firewall that breaks out to a provider’s points of presence, while larger sites may still warrant traditional firewalls. This is exactly where a partner like Technium adds value — helping map the existing architecture, identifying where SASE is genuinely a good fit, designing how the overall environment will interact, and phasing in complex rollouts to minimize risk. The goal is to understand, and plan for, the full picture before selecting or deploying any technology.
Grounding the process in requirements and risk, rather than getting drawn in by whichever product has the most features, is the most important first step you can take.
Step-by-Step Assessment Plan
| Step 1: Leave Technology Out of It — For Now Start with strategy, not products. Define your goal before evaluating anything else. |
| Step 2: Assess Your Current Infrastructure Map your sites, what happens at each one, what connectivity is needed, and how users traverse the network. |
| Step 3: Build Out Your Requirements Separate non-negotiables from nice-to-haves. This keeps your evaluation grounded and vendor-neutral. |
| Step 4: Understand How Risk Is Shifting A transition changes the nature and location of risk — not just whether it exists. Know what you’re accepting. |
| Step 5: Right-Size the Solution for Each Location Smaller sites may need only a stripped-down firewall. Larger sites may still warrant traditional infrastructure. Design accordingly. |
| Step 6: Evaluate Technology Last Few tools cover every piece of the puzzle. Let your requirements lead the selection — not the other way around. |
How do you know if this new architecture is working? Success metrics depend on the organization’s primary goals going in. Common objectives include cost reduction — eliminating MPLS costs being the obvious one — architecture simplification, like consolidating firewall and MPLS functions into a single point of presence, improved user access and responsiveness, and ease of provisioning and ongoing user management. At the end of the day, the key question is whether the transition was implemented seamlessly, and whether users can get what they need without friction.
Looking Ahead
Modern networks require modern architectures. Moving beyond MPLS isn’t just upgrading connectivity, it’s aligning your network infrastructure to how your business actually operates. The shift from perimeter-based trust to continuous, identity-based verification is paramount to the “secure business anywhere” mindset.
“SASE is widely regarded as a sound, logical long-term direction — especially for organizations with multiple sites, remote workforces, and cloud-heavy environments. It’s a direction I think a lot of companies are going to continue moving toward.” – Michael Joseph, CEO, Technium
The shift from MPLS to SD-WAN and SASE isn’t just a technology upgrade — it’s a fundamental rethinking of where trust lives in your network. Instead of relying on fixed, dedicated links between known locations, organizations are learning to verify continuously, govern access granularly, and extend security to wherever people actually work.
This isn’t a transition to rush into for the sake of keeping up with the industry. It’s one to approach deliberately — starting with a clear-eyed assessment of your architecture, requirements, and risk tolerance, long before any technology decisions are made. For organizations with multiple sites, distributed workforces, or cloud-heavy environments, SASE isn’t just a trend to watch. It’s a sound, logical direction — and one that genuinely makes “secure business anywhere” possible.
For more, visit Technium’s website.


